Connecting to AI Services
Integrating AI into IFS Cloud Remote or Remote-Hybrid deployment is essential to unlock the full suite of advanced capabilities embedded in the platform. Access to Copilot for contextual assistance within workflows, predictive analytics to support data-driven decision-making, and intelligent automation that streamlines complex operational processes.
This guide provides instructions for connecting an existing remotely deployed IFS Cloud environment to the AI platform as a tenant.
Overview
The integration between IFS Cloud and IFS AI platform enables secure communication via modern OAuth 2.0 authentication mechanisms between IFS Remote Tenants and IFA AI Services. Once configured, your deployment can take full advantage of AI-powered features that play a critical role in optimizing deployment efficiency, scalability, and long-term value.
Prerequisites
Ensure the following conditions are met before proceeding with the configuration:
- IFS Cloud Version: The deployment must be on version 25.1.1 or later.
- Network Access: The deployment must not be air-gapped; it must allow outbound communication to IFS AI URLs from the IFS Cloud application.
- Entitlements: All necessary entitlements for AI capabilities must be purchased.
- Access Studio Setup: Access Studio must be registered and configured.
- Tenant Provisioning: A tenant must be successfully provisioned via Access Studio, and the following must be obtained:
- Tenant URI
- One-time token
For details on provisioning tenants and setting up Access Studio, please refer to the official ALE documentation.
Configuration Steps - Connecting to IFS AI
To integrate your remotely deployed IFS Cloud environment with the IFS AI platform, follow these steps:
1. Update Installer Configuration
In your installer configuration file (ifscloud-values.yaml), add the following parameters:
| accessStudioUrl | Tenant URL copied from Access Studio |
| accessStudioNonceKey | One-time token (nonce) received from Access Studio |
| deploymentModel | Set to REMOTE |
| nxsUri | for EU region: https://plt-eu.nxs.ifs.cloud for US region: https://plt-us.nxs.ifs.cloud |
| mlServiceApi | api://prd.ifsmlservice.ifs.cloud |
| xdivServiceApi | api://prd.xdiv.ifs.cloud |
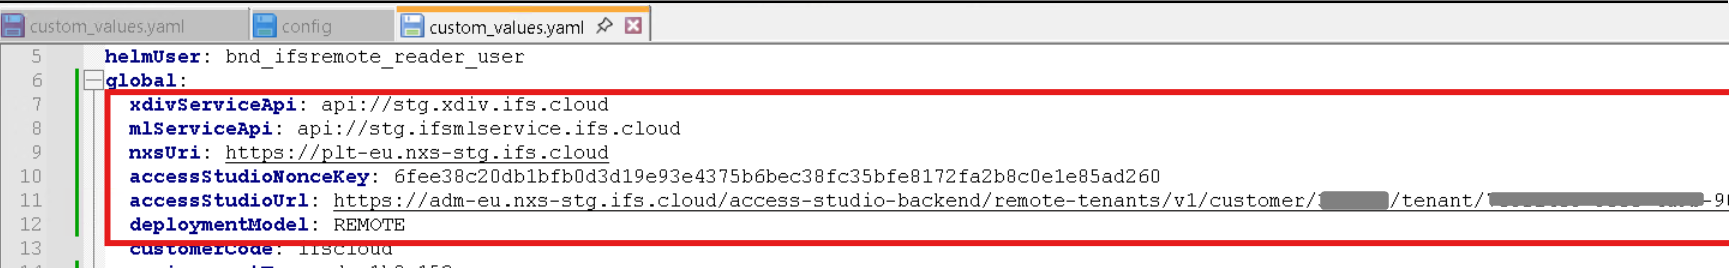 This is an example installer configuration file that represents the specified parameters.
Ensure all values are accurate and securely stored. The One-time token is tenant-specific and valid for 24 hours only.
2. Run Middle-Tier Installation
With the configuration in place, rerun the middle-tier installer to apply the changes.
Execute the following commands:
For further details, refer to the Installer Actions document.
A full restart is required because all IFS Cloud pods must reload the updated configuration.
IMPORTANT!
Every time the IFS AI configuration is updated and the installer is run, the relevant IFS Cloud pods must be restarted in order to fetch the latest credentials from the IFS AI platform. Without restarting the pods, the updated AI credentials will not be picked up and the integration will remain inactive.
During this process:
- The One-time token (valid for 24 hours and unique to each tenant) is exchanged for a refresh token with extended validity (typically up to 6 months).
- The installer creates a Kubernetes secret named Nexus Access Studio, containing:
- The refresh token
- The updated tenant URI
This enables secure authentication between IFS Cloud services and the IFS AI platform via Curity.
Token Management
Validity & Rotation
- Refresh Token Validity: 6 months
- Automatic Rotation: When valid Nexus authentication credentials are available, the installer automatically refreshes and rotates tokens during upgrade. If the required authentication secrets are no longer available, a new One-time Token must be generated from Access Studio and supplied during installation.
Secure Storage Requirements
The refresh token must be securely stored using one of the following:
- Enterprise Vault (e.g., HashiCorp Vault)
- Kubernetes Secret (ensure encryption at rest is enabled)
Post-Onboarding
Once onboarding is complete, the remote IFS Cloud environment is fully connected to the IFS AI platform. Users can now begin leveraging AI-enhanced services, driving smarter workflows, deeper insights, and operational efficiencies.
Release Updates and Service Updates
During a Release Update or a Service Update installation, the installer attempts to use the existing Access Studio authentication data to communicate with the IFS AI platform and update the tenant configuration.
When existing secrets are preserved
If the Kubernetes secret created during the initial onboarding is still available:
- No new One-time Token is required.
- The same values previously configured in
ifscloud-values.yamlcan be reused. - Running the installer is sufficient.
- The installer automatically handles the tenant version update and token refresh process.
When existing secrets are removed
Some upgrade or environment recreation scenarios may remove Kubernetes resources, including the nxs-access-studio secret. If the secret is no longer available, the installer cannot retrieve the required authentication data and may fail with errors.
In this scenario:
- Generate a new One-time Token from Access Studio.
- Update the accessStudioNonceKey value in
ifscloud-values.yamlfile. - Run the installer.
IMPORTANT
A new One-time Token is only required when the existing Access Studio authentication data is no longer available, for example after cluster recreation or deletion of the associated Kubernetes secrets. If the existing authentication secret is preserved, the installer can continue using the previously configured values and no new One-time Token is required.